Directory / plugin
RefiTune – Site refiner toolkit
v1.4.0 · by Tamas Rottenbacher
Take control of WordPress with smart performance tweaks, security enhancements, and usability improvements. RefiTune is an all-in-one toolkit.
About this plugin
Hungarian: Magyar nyelvű bővítmény leírás
RefiTune – Site refiner toolkit is a modular Swiss Army knife for WordPress. Clean up unnecessary front-end code, harden login and uploads, tune Heartbeat and updates, or brand wp-login – each module is opt-in.
Enable or disable features individually. A clean dashboard shows what is active. In-plugin Help pages document behaviour, trade-offs, and requirements.
What’s Inside? (37 Modules)
Performance:
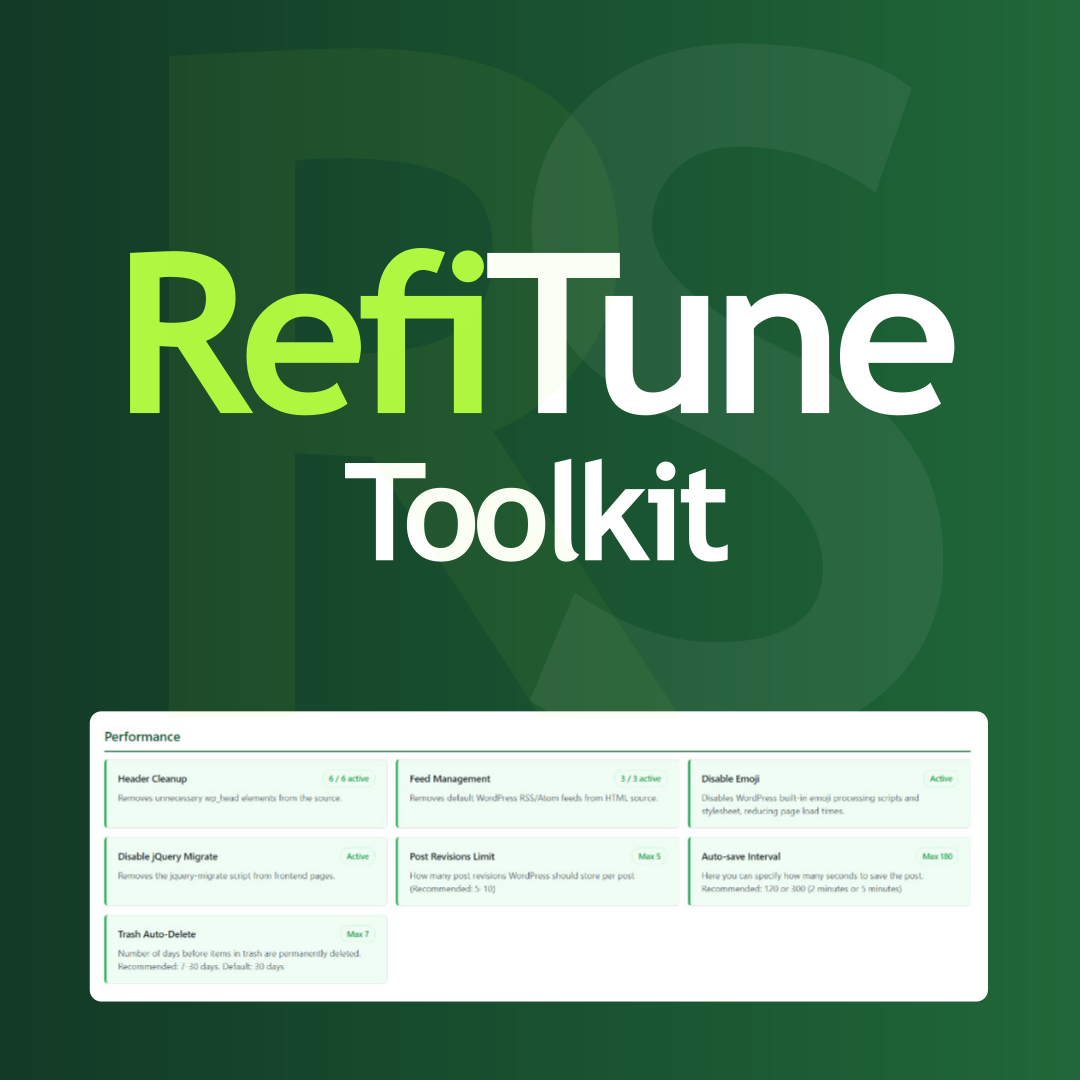
* Header Cleanup – Strip unnecessary wp_head output for leaner pages.
* Feed Management – Control RSS/Atom feed link tags in the document head.
* Disable Emoji – Remove WordPress emoji scripts and styles.
* Disable jQuery Migrate – Drop legacy jquery-migrate when your stack does not need it.
* Disable oEmbed – Stop automatic embeds from pasted YouTube, Vimeo, Twitter/X, and similar URLs.
* Remove Asset Version Query Strings – Strip ?ver= from front-end CSS/JS (can break cache busting; prefer CDN purge or hashed filenames). Locked when WP_CACHE is true in wp-config.php.
* Post Revisions Limit – Cap stored revisions per post. Locked when WP_POST_REVISIONS is defined in wp-config.php.
* Auto-save Interval – Change how often the editor auto-saves. Locked when AUTOSAVE_INTERVAL is defined in wp-config.php.
* Trash Auto-Delete – Set trash retention; expired items are removed in batches so large queues stay memory-safe. Locked when EMPTY_TRASH_DAYS is defined in wp-config.php.
* Convert Uploads to WebP – Convert JPEG/PNG to WebP on upload, optional max size resize, then remove the original (GD or Imagick with WebP; uses unique filenames and refuses unsafe overwrites).
* Heartbeat API Control – Tune or disable Heartbeat in admin, front end, and the post editor.
* Resource Preload – Add early link rel="preload" hints for internal site assets by location (everywhere, front page, blog, or post ID), with as, type, crossorigin, and fetchpriority. Optional one-click import of active WordPress Font Library fonts (AJAX on demand).
Security:
* Hide Generator Tags – Remove WordPress (and WooCommerce, when active) version meta tags.
* Disable XML-RPC – Respond to XML-RPC with 404 and remove RSD discovery.
* Disable Trackback/Pingback – Close pings and strip pingback methods/headers.
* Disable File Editor – Set DISALLOW_FILE_EDIT so theme/plugin editors stay off. Locked in the UI when the constant is already defined in wp-config.php.
* Automatic Updates Control – Tri-state plugin, theme, translation, and core updates; reschedule update checks. Respects AUTOMATIC_UPDATER_DISABLED (full lock) and WP_AUTO_UPDATE_CORE (core-only; plugins/themes/translations and update checks stay configurable).
* Login Error Messages – Generic login errors to reduce username enumeration.
* Restrict Admin Access – Choose which roles may open wp-admin UI. Users with manage_options always keep access. Front-end admin-ajax.php is intentionally not blocked.
* REST API Restrictions – Limit selected core REST routes to users with manage_options.
* Login Limit – Rate-limit failed logins by IP and IP+username pair (REMOTE_ADDR only). Optional IP whitelist (one address per line). Covers wp-login.php and other wp_signon() paths (including WooCommerce).
* Verified Upload – Block disguised uploads: double extensions, MIME/magic mismatches, and script markers.
Visual:
* Hide Admin Bar – Hide the admin bar for selected roles.
* Block Visibility (Mobile) – Per-block always / mobile-only / desktop-only via wp_is_mobile(); omits HTML server-side; sends Vary: User-Agent (full-page caches must honour it). Also available in the core Hide block modal.
* Block Visibility (Roles) – Per-block visibility for guests, logged-in users, or selected roles; omits HTML server-side. Shares the Visibility panel and Hide block modal with the mobile module.
* Login Page Customization – Brand wp-login.php with logo and colours.
Email:
* Email Notifications – Disable or redirect selected WordPress system emails.
* Email sending – SMTP with encrypted password storage, or disable all site emails. In production, disabling TLS/certificate verification is blocked.
Miscellaneous:
* Disable Comments – Site-wide comments off (optional WooCommerce review keep).
* External Links in New Window – Open external links in a new tab with safe rel attributes.
* Enable Page Excerpt – Excerpt support for pages.
* Clean Upload Filenames – Sanitize upload filenames (accents, spaces, special characters).
* SVG Upload – Role-gated SVG uploads with allowlist-based sanitization (XXE-safe parse).
* AVIF Upload – Role-gated AVIF uploads (full core AVIF support needs WordPress 6.5+).
* Role Redirects – Per-role login and logout redirect URLs.
* Maintenance Mode – 503 maintenance page for guests; chosen roles keep access. Admin, AJAX, and cron stay available so staff can work.
* Dynamic Year Shortcodes – [refi-year] and [refi-year from="2006"].
More plugins: rotistudio.com
Author site: rottenbacher.hu
GitHub: github.com/rotisoft/refitune
Translations
- English (default – source strings in code and
refitune.pot) - Hungarian (Magyar) –
refitune-hu_HU.po(compile to.mofor WordPress to load)
Contribute translations under /wp-content/plugins/refitune/languages/. Text Domain: refitune.